Security News

Flock CEO defends surveillance technology

Flock CEO Defends AI Surveillance Technology Amid Growing Privacy Backlash: “We Shouldn’t Pause Progress”

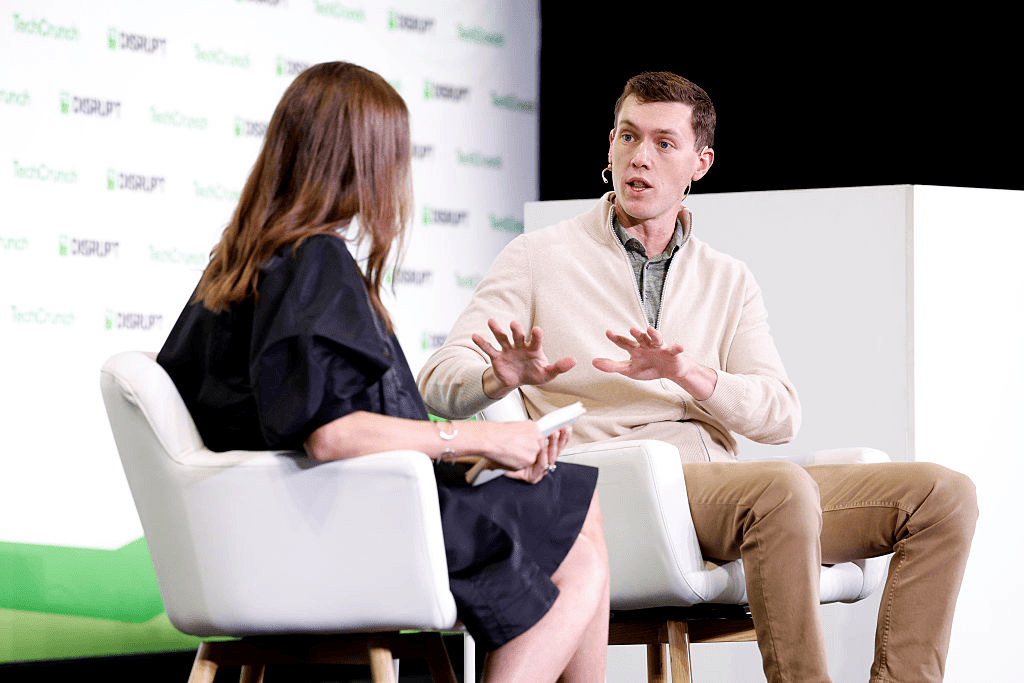
Flock Safety CEO Garrett Langley is defending the company’s surveillance technology as growing public opposition raises questions about privacy, artificial intelligence, and the expanding use of automated license plate readers across the United States. In an October 14, 2026, report, TechCrunch highlighted Langley’s response to the mounting criticism, including concerns about how surveillance systems collect and share data. His position centers on the argument that technological progress should continue despite the controversy surrounding its use. The debate puts Flock Safety at the center of a broader national discussion about public safety, digital privacy, and the limits of surveillance technology. Why Flock Safety Is Facing Growing Backlash Flock Safety develops surveillance systems used by law enforcement agencies, businesses, and communities. Its technology includes automated license plate readers that capture vehicle information and help investigators search for vehicles connected to reported crimes. Supporters argue these systems can help police investigate thefts, identify suspect vehicles, and respond to public safety incidents more efficiently. However, critics question how extensively authorities should track vehicle movements and what safeguards protect information collected by these networks. Privacy advocates have also raised concerns about data retention, access controls, information sharing between agencies, and the potential for surveillance tools to be used beyond their original purpose. These concerns have fueled public scrutiny of Flock Safety and other companies developing AI-powered surveillance products. Flock CEO Says Surveillance Technology Should Keep Advancing Speaking at TechCrunch Disrupt 2026 in San Francisco, Langley argued that surveillance technology can improve accountability by helping law enforcement identify vehicles connected to criminal investigations. His remarks reflected the company’s position that the potential public safety benefits justify continued technological development. However, during the discussion, he faced questions about the criticism directed at Flock and the real-world risks associated with its products. Privacy Concerns and Contract Cancellations Put Pressure on Flock The backlash has had practical consequences for the company. Some communities have reconsidered or cancelled their contracts, while concerns about improper access to surveillance databases have intensified scrutiny of Flock’s operations. Critics argue that automated license plate readers can create detailed records of people’s movements, including those of individuals who have not been accused of any crime. They want stronger restrictions on data access, retention, and sharing. Supporters, meanwhile, point to the potential for these systems to help investigators locate stolen vehicles and develop leads in criminal cases. The central challenge is determining how to preserve those benefits while protecting civil liberties. The Future of AI Surveillance in the United States The debate surrounding Flock Safety highlights a wider technology industry challenge: innovation must contend with public trust, privacy rights, and accountability. As AI-powered cameras and connected surveillance networks become more widespread, communities are likely to continue examining who can access collected data, how long it remains stored, and what oversight prevents misuse. For Flock, Langley’s message is clear: technological progress should continue. Whether that position reassures communities will depend in part on how effectively the company and its customers address concerns about surveillance and data protection.Source: TechCrunch.
Flock CEO Defends AI Surveillance Technology Amid Growing Privacy Backlash: “We Shouldn’t Pause Progress” Read More »

, , , , , , , , , , ,
encryption-lock-techmeo-com

WireGuard Update Crisis: Microsoft Lockout Blocks VPN Security Fixes for Windows Users

A major disruption in the cybersecurity world has raised alarms across the tech industry. Popular open-source VPN project WireGuard is currently unable to deliver updates to Windows users after its developer account was unexpectedly restricted by Microsoft. What Happened to WireGuard? Jason Donenfeld, the creator of WireGuard, revealed that he has been locked out of his Microsoft developer account. This access is essential for signing drivers and pushing updates to Windows systems. Without this authorization: Donenfeld described receiving an “access restricted” error just as he was preparing to submit a new update. Why This Lockout Matters for Cybersecurity WireGuard is widely trusted for its speed, simplicity, and strong encryption, forming the backbone of several major VPN services like Mullvad VPN and Tailscale. If developers cannot push updates: Donenfeld even warned that in a worst-case scenario, users could be exposed if a critical vulnerability emerged during the lockout period. Microsoft’s Verification Policy at the Center The issue appears linked to Microsoft’s Windows Hardware Program, which requires developers to verify their identity before publishing drivers. This program ensures that only trusted developers can deploy software with deep system access. However: Despite successfully verifying his identity through official channels, Donenfeld’s access remains restricted. Not an Isolated Incident WireGuard is not alone. Other high-profile projects are facing similar issues: This pattern suggests a broader problem affecting multiple developers relying on Microsoft’s ecosystem. Delays, Frustration, and Uncertainty According to Donenfeld, Microsoft’s support response has been slow. Even after escalating the issue to executive support, resolution could take up to 60 days—a significant delay for security-critical software. The lack of communication has frustrated developers, with some openly criticizing the support process and lack of transparency. A Glimmer of Hope By midweek, Donenfeld confirmed he had finally established contact with Microsoft, raising hopes that access may soon be restored. However, no official statement has been released by the company. What This Means for Windows Users This situation highlights a critical dependency in the tech ecosystem: Final Thoughts The WireGuard lockout underscores the delicate balance between platform security policies and developer access. While verification systems aim to protect users, sudden account suspensions without notice can create unintended risks. The source of this news is Tech Crunch. For readers of TechMeo, this incident is a stark reminder: even the most trusted security tools depend on infrastructure that can fail unexpectedly—making transparency and communication more critical than ever.

WireGuard Update Crisis: Microsoft Lockout Blocks VPN Security Fixes for Windows Users Read More »

, , , , ,
cyber-hacker-techmeo-com

Close to $1M Cyber Heist: Hacker Diverts £700,000 from Energy Firm in Sophisticated Payment Scam

A shocking cybercrime incident has exposed the growing threat of financial fraud in the digital age. UK-based energy company Zephyr Energy confirmed that hackers successfully redirected a payment worth £700,000 (nearly $1 million) into a fraudulent account—raising serious concerns about business cybersecurity. How the Cyberattack Happened According to a regulatory filing, the stolen funds were intended for a legitimate contractor working with Zephyr’s U.S. subsidiary. However, cybercriminals intercepted the transaction and rerouted the payment to an account under their control. While the company has not disclosed the exact entry point, experts believe this type of attack typically involves business email compromise (BEC)—a method where hackers gain access to corporate emails or financial systems to manipulate payment details. Business Email Compromise: A Growing Threat Business email compromise attacks are among the most damaging cyber threats today. The Federal Bureau of Investigation (FBI) reports that BEC scams caused over $3 billion in global losses in 2025 alone, making them one of the top cybercrime categories. These attacks often involve: The Zephyr case highlights how even established companies can fall victim to these highly targeted scams. Company Response and Recovery Efforts Zephyr Energy stated that it is actively working with banks and cybersecurity consultants to recover the stolen funds. The company also assured stakeholders that: Despite following “industry-standard practices,” the breach underscores the need for constant upgrades in cybersecurity infrastructure. What This Means for Businesses This incident serves as a wake-up call for companies worldwide, especially those handling large financial transactions. Key cybersecurity takeaways include: Final Thoughts The £700,000 cyber theft targeting Zephyr Energy is a stark reminder that no organization is immune to digital fraud. As cybercriminals become more sophisticated, businesses must stay proactive to protect their financial systems and sensitive data. The source of this news is Tech Crunch. For readers of TechMeo, this story highlights a critical reality: in today’s connected world, cybersecurity is no longer optional—it’s essential.

Close to $1M Cyber Heist: Hacker Diverts £700,000 from Energy Firm in Sophisticated Payment Scam Read More »

, , , , ,